
Embed Breach Intelligence in Your Security Product
REST API and SDKs ready for production from day one: public pricing, one signed partner agreement.
Need a hand integrating?

xonThreatIntel+ or xonAPI+?
Both are breach APIs. They answer different questions.
THIS PAGE
xonThreatIntel+
For security products that need domain-level breach information. Onboard your customers' domains, pull each domain's breach summary, and get alerted when new exposure lands.
Priced by domains monitored, from $99/mo. Email checks are included on the same key.
More than 50 customer domains? Scale plans run from 50 domains to thousands, with volume discounts.
ALSO AVAILABLE
xonAPI+
For checking one email address at a time, at sign-up or login. No domains to onboard.
Priced by request rate, from $9/mo.
See xonAPI+Built for Security Platforms & Product Teams
Production-ready breach intelligence, designed for embedding
Built for Multi-Tenant Scale
Manage hundreds of customer domains with tenant-level isolation. Each tenant gets independent alerting rules, watchlists, and reporting.
API-First With Full Specs
REST API with <100ms response, webhook delivery, and 99.99% uptime SLA. Official SDKs in 8 languages.
Live the Same Day
Self-serve checkout and one signed agreement. Add a client domain and its dashboard populates in one to three minutes.
JSON + CSV Feeds
Choose your delivery format. JSON for SIEM and data-lake ingestion, CSV for reporting and client hand-offs. Both fully documented.
Zero Query Persistence
Email and domain lookups are processed in memory. The identifiers your platform sends are never logged or stored; only request metadata is kept for billing and abuse prevention.
Predictable Monthly Billing
Flat monthly rates with no per-request overages. Cancel anytime, no annual contracts, no surprise bills at month-end.
How Platforms Use xonThreatIntel+
Three ways security platforms surface breach intel to their customers
Embed in customer dashboards
Show clients which of their domains and accounts appear in breaches, alongside the other risk signals you already surface. Your UI, your branding, your context.
Enrich your scheduled reports
Add breach context to the recurring customer reports you already generate. No new pipeline to maintain, no breach index to keep fresh.
Inform analyst workflows
Give SOC analysts the full breach history for any domain or email. They decide remediation based on the client's incident-response runbook, not ours.
Pull a Domain's Exposure, Get Pushed What's New
One call returns the breach summary for a customer domain. A webhook tells you when it changes.
curl -G \
  "https://plus-api.xposedornot.com/v2/partner/domain-summary" \
  -d domain=example.com \
-H "x-api-key: YOUR_API_KEY"{
"domain": "example.com",
"breach_count": 15,
"Yearly_Metrics": { "2023": 8, "2024": 5, "2025": 2 },
"Domain_Summary": { "example.com": 1250 },
"Top10_Breaches": {
"AnotherBreach": 750,
"ExampleBreach": 500
},
"Detailed_Breach_Info": {
"ExampleBreach": {
"breached_date": "2023-01-15",
"xposed_data": "Email addresses;Passwords",
"xposed_records": 5000000
}
},
"Seniority_Summary": {
"executive": 3,
"manager": 12,
"individual_contributor": 47
}
}{
"event": "new_findings",
"as_of": "2026-08-29T10:15:00+00:00",
"domains": [
{
"domain": "examplecorp.com",
"new_breaches": ["ExampleBreach"],
"new_records": 42
}
]
}- Sent when a new breach touches any domain on your account.
- Signed with HMAC-SHA256 over the raw body.
- No email-level data travels in it. Read as_of, then call domain-summary with it as since.
Full field reference and error codes in the Partner API docs.
Ship Breach Detection in Hours, Not Months
Sign the partner agreement and DPA once, then onboarding is self-serve: API credentials, production SDKs, and full docs, live the same day.
30 minutes
Test Your Integration
Make live API calls from your dev environment. Same endpoints and response shape your customers will see.
Typically 2–4 hours
Integrate & Ship
Add to your product with official SDKs in 8 languages. Solutions engineer available. Or skip the code: connect an MCP client to
https://plus-api.xposedornot.com/mcpwith your key and the eight tools are live in your agent in under a minute.
What You Get on Day 1
Same kit on every plan. Five things come with your account from the first day.
See partner plansProduction API key
IncludedLive access to v3 endpoints with per-key analytics and audit logs.
Partner console
IncludedWeb dashboard for key management, usage analytics, and rate-limit headroom.
SDKs & docs
IncludedOfficial SDKs in 8 languages on the major package registries. Full reference at console.xposedornot.com/docs/api.
Concierge onboarding
Included30-min call with our partner team to walk through credentials, your stack, and first integration.
MCP endpoint
IncludedThe same production key works in your AI tooling from day one. One
claude mcp addline or a six-line JSON block; setup for every client is on the docs page.
What We Commit To
Coverage and SLAs you can build on
Independently monitored, measured monthly. Credit-backed on Ultimate and enterprise plans.
For onboarded domains: from a breach landing in our index to your notification, by email or webhook.
Continuously growing. Only breaches that are already publicly available, verified before they are indexed.
Public disclosures, paste sites and dumps that have surfaced on public channels. Never purchased from threat actors.
Feeds available in JSON and CSV, with webhook delivery as soon as a breach lands in our index.
Uptime is independently monitored: see the live status page · full SLA terms
Built for Production
Rate limits, webhooks, audit logs and the integrations your team will ask for
Rate Limits & Headers
Standard 429 responses include retry-after headers. Per-key request analytics in the partner console so you can right-size your usage.
Key Scoping & Audit Logs
Restrict API keys to specific IP ranges or environments, and rotate or revoke them from your partner console without ticketing. Every request is logged with timestamp, key, and response status.
Webhook Delivery
Breach alerts pushed to your endpoint as JSON, within 15 minutes of a breach landing in our index. Available on Growth and Ultimate plans, configurable per client. We've written up what real time actually means in a dark web monitoring API.
Structured Errors
Consistent JSON error schema with status and message fields, mapped to standard HTTP codes. Predictable handling across every endpoint.
SIEM Integrations
Native Splunk and Microsoft Sentinel integrations run the scheduled sync for you. Everything else takes the REST API or JSON and CSV feeds.
Alert Channels
Besides webhooks, alerts go out by email, Slack and Teams, so your own team hears about a customer's exposure the same way your product does.
Side by Side With Legacy Vendors
Where xonThreatIntel+ wins and where legacy slows you down
Enterprise-grade breach data at a fraction of legacy threat-intel pricing, starting at $99/mo. Card checkout, partner agreement and DPA signed during onboarding. Most partners onboard the same day.
What customers are saying
Verified reviews from G2
Sundar Kumar
IT and Product Head, Corent Technology
"Xposedornot is a useful tool for data breach alerting system. Every organization requires this tool to receive timely alerts of their exposed breaches. Its user-friendly design and seamless integration make it a valuable asset for proactive data security."
Miguel Mendes
IT Security Lead, Bluecom
"Indispensable to monitor the exposure of your personal data. What I like most about ExposedOrNot is its real-time dashboard alerts, as well as integration with Slack and Teams, are very practical features to be informed immediately in the event of a compromise."
Bertold Kolics
VP Engineering, Verosint
"I have been working with XposedOrNot from the early days. My experience could not have been better. The service scales well, performs well under high load and it has a large set of breach data dating back to several years."
Senthil K
Information Security Officer, Invicara
"I love how XposedOrNot makes protecting our data so simple and effective from ATO. The alerts are timely, and the CXO dashboard gives a clear picture of breach trends and risks. It's more than just a tool, it's like having a personal assistant for your security."
Plans That Scale With Your Client Base
Start with 10 domains at $99/mo. Add more as you grow. Scale plans from 50 domains to thousands
Basic
Growth
Ultimate
| Compare plans | Basic $99 /mo | MOST POPULAR Growth $243 /mo | Ultimate $447 /mo |
|---|---|---|---|
| Domains monitored | 10 | 25 | 50 |
| Data delivery | API + CSV | API + JSON + CSV | API + JSON + CSV |
| Alerts after indexing (<15 min) | Email + webhooks | Email + webhooks | |
| CXO dashboards | |||
| Deep dive analysis | — | ||
| Support response | Email (next business day) | Slack + email (same day) | Priority (4 business hours) |
| Custom integration support | — | — | |
| Threat intel advisory sessions | — | — | |
| 99.99% uptime SLA | Standard | Standard | Credit-backed |
All plans include: cancel anytime, monthly billing, and a 30-day money-back guarantee. Checkout is self-serve and onboarding starts immediately, so most partners are live the same day.
- Everything in Ultimate
- Volume discounts from 50 domains
- One partner agreement across the whole portfolio
- Invoice billing and annual terms available
By purchasing you agree to our Terms of Service and Privacy Policy.
For comparison: SpyCloud's MSSP program is sales-gated with no published pricing. Resale rights and multi-tenant access are included in every xonPlus tier.
Frequently Asked Questions
Everything about integration, pricing, and going live
Reselling breach monitoring to your clients instead? See xonThreatIntel+ for MSSPs →
From the blog
All posts →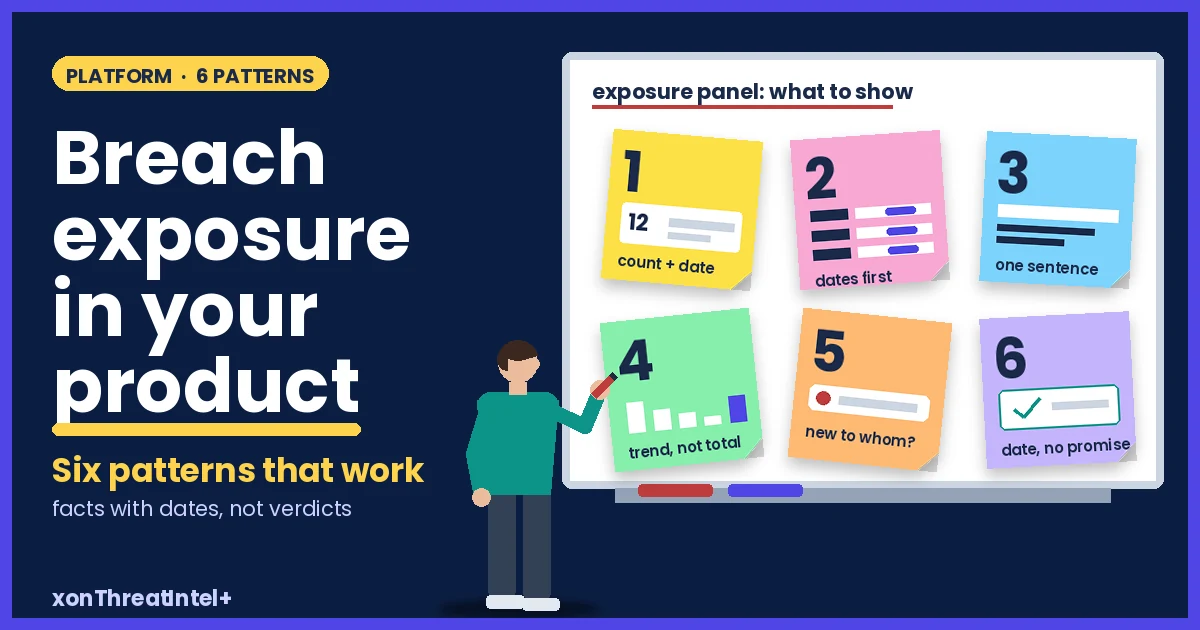
Breach Exposure in Your Product: 6 Patterns That Work
Show facts, not verdicts. A count and a date, a dated list with chips, one plain sentence per breach, the trend rather than the total, what's new to the index, and an empty state that promises nothing. Each pattern tied to the API field it's built from.
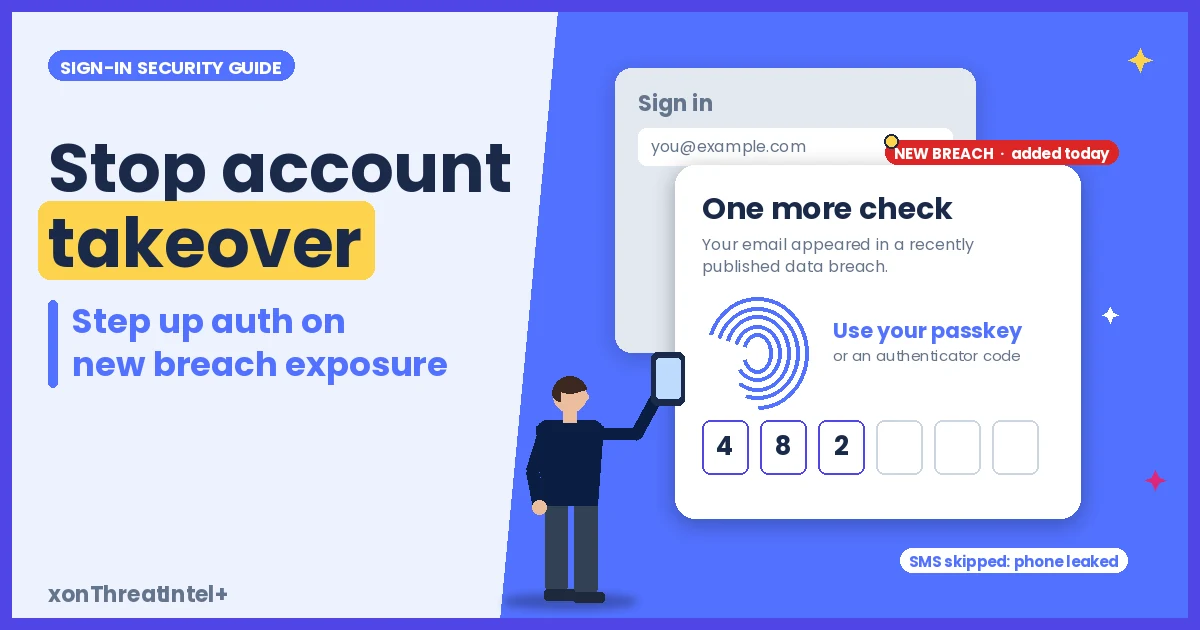
Stop Account Takeover: Step Up Auth on New Breach Exposure
When a user's email lands in a newly indexed breach, ask that one account for a stronger check at its next sign-in, and leave everyone else alone. The research, 149 breaches added in a year, what leaked decides the factor, a policy you can ship, and two ways to wire it.
xonThreatIntel+ Is Now an MCP Server for AI Agents: Eight Tools, One Key
A hosted MCP server on your existing partner key: eight tools, nothing to install, writes gated by a confirm flag. Why the webhook tool was left out, and how to connect Claude Code or Cursor.
Put Domain Breach Intelligence in Your Product
Build breach detection into your product with our API. Official SDKs in 8 languages. 30-day money-back guarantee.